About · who runs Faultline
A working bug
bounty hunter.
I'm Igor Yakunin. I find security bugs on live platforms for a living: broken access control, authentication bypasses, exposed secrets. This year my targets moved to AI platforms. Faultline applies the same discipline to AI agents: reproduce the failure, check the fix, keep the test.
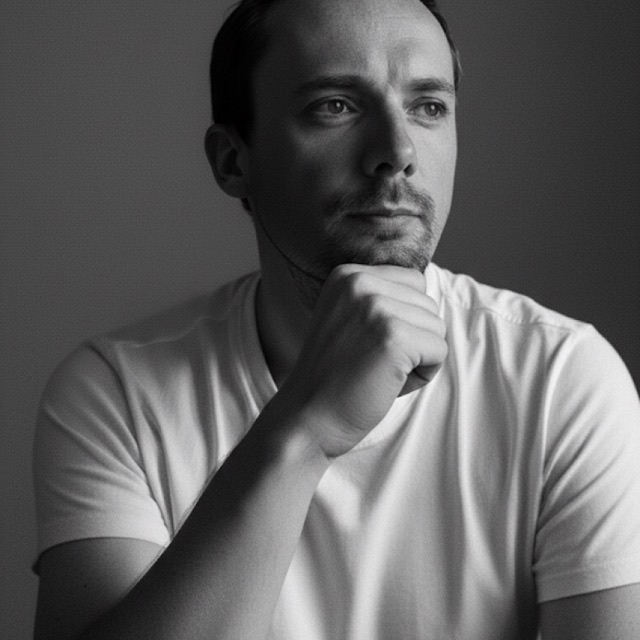
Prague, Czech Republic
Numbers from my public Hackrate profile, 20 October 2026. The global rank updates daily.
01 / WHERE I HUNT
Where the bugs
come from.
My accepted findings cluster in a few familiar places. Counts are the top weakness families from the profile.
02 / AI PLATFORMS
Last year, mostly
AI platforms.
Most of my paid findings last quarter were on AI products. Program names stay private. What each product does, and what I found there.
- An AI code editor
Document-content IDOR in the editing flow.
- An AI recruiting platform
Cross-tenant account-takeover chain.
- An AI ERP suite
UI-model authorization bypass.
- An insurance chatbot
Chatbot and OAuth weakness.
ALSO FILED · ANTHROPIC
I've also filed reports against Anthropic: a Claude Code managed-policy bypass, an MCP approval flaw, and an MCP OAuth issue on api.anthropic.com. Some are still in triage or disputed, and one was a confirmed duplicate of a CVE already fixed upstream.
03 / THE TEAM
Not a one-man show.
The other people on the team are professionals in their own fields. When you write to Faultline, you talk to me directly, and the work goes to whoever does it best.
Faultline is new. The testing method is built and verified locally. The bounty record above is real, and it's the standard I hold the work to.
LET'S START WITH ONE CASE
What went wrong?
What should have happened?
Igor · Prague, Czech Republic · No credentials or private logs, please.